
Stop phishing the moment it lands.
Prove your controls the moment auditors ask.
Cordon analyzes every email in real time, contains threats autonomously within guardrails you control, and turns every detection into audit-ready evidence, mapped to MITRE ATT&CK, NIST CSF, ISO 27001, and SOC 2.
From PayPal Support <billing-support@paypa1-secure.com>
Urgent: Verify your account within 24 hours
Risk score
100/100
Top indicators (9 total)
- Credential-harvesting language detected
- Brand name used in an unrelated domain
- Link display text does not match its destination
Mapped to compliance frameworks
Every detection maps to
Watch the full Cordon walkthrough
A 90-second walkthrough: detection, early warning, staff training, and audit-ready compliance.
Try it on a real email
Pick a sample email below and click Analyze to watch Cordon’s real verdict render.
From: PayPal Support <billing-support@paypa1-secure.com>
To: employee@ourcompany.example
Subject: Urgent: Verify your account within 24 hours
This email has not been analyzed yet. Click below to run it through Cordon.
Real Cordon analysis on curated sample emails. Live, paste-your-own analysis is coming soon.
One platform, one AI engine
Every detection surface shares the same reasoning engine, the same evidence trail, and the same guardrails.
Phishing Analysis
Deterministic and LLM-assisted analysis of headers, links, attachments, and auth results. Malicious verdicts in under 2 seconds.
AI-Attack Detection
Cordon's AI reasons about the intent behind a message, catching AI-generated and polished social-engineering lures that pattern-matching misses, as a bounded signal that supports the verdict without ever overriding the deterministic core.
Intrusion & Exfiltration
Behavioral baselines (UEBA) catch impossible travel, brute force, mass access, and data exfiltration, tuned to each user's normal, not a static rule.
Compliance Evidence
Every detection auto-maps to MITRE ATT&CK, NIST CSF 2.0, ISO 27001, and SOC 2, exportable as a signed audit pack.
Analyst Copilot
Ask questions of your own threat data in plain English. Cordon's copilot answers from your cases and events, not the open internet, so "which accounts had failed logins this week" becomes a straight answer.
Continuous Control Monitoring
Cordon watches whether each compliance control is still producing evidence and flags control drift the moment coverage lapses, so an audit gap surfaces when it happens, not at audit time.
Threat Intelligence
Every sender, link, domain, and IP is checked against known-bad threat-intel feeds. A match against real attacker infrastructure raises the verdict on its own, with the feed and date cited as evidence.
Security & Compliance Reporting
One click turns Cordon's detections, risk, and control coverage into a board- and auditor-ready report, mapped to ISO 27001, NIST CSF, SOC 2, and MITRE ATT&CK, and exportable as a branded PDF. The work that protects you, packaged as the evidence that proves it.
Catches phishing like a top analyst. Reports it like an auditor.
Catches hidden AI-injection attacksNew
Attackers now hide instructions inside emails — invisible text, zero-width characters, and encoded payloads — to hijack the AI assistants that read your inbox. Cordon inspects the raw email, flags these hidden-instruction payloads, and maps them to MITRE ATT&CK.
What a Security & Compliance Report looks like
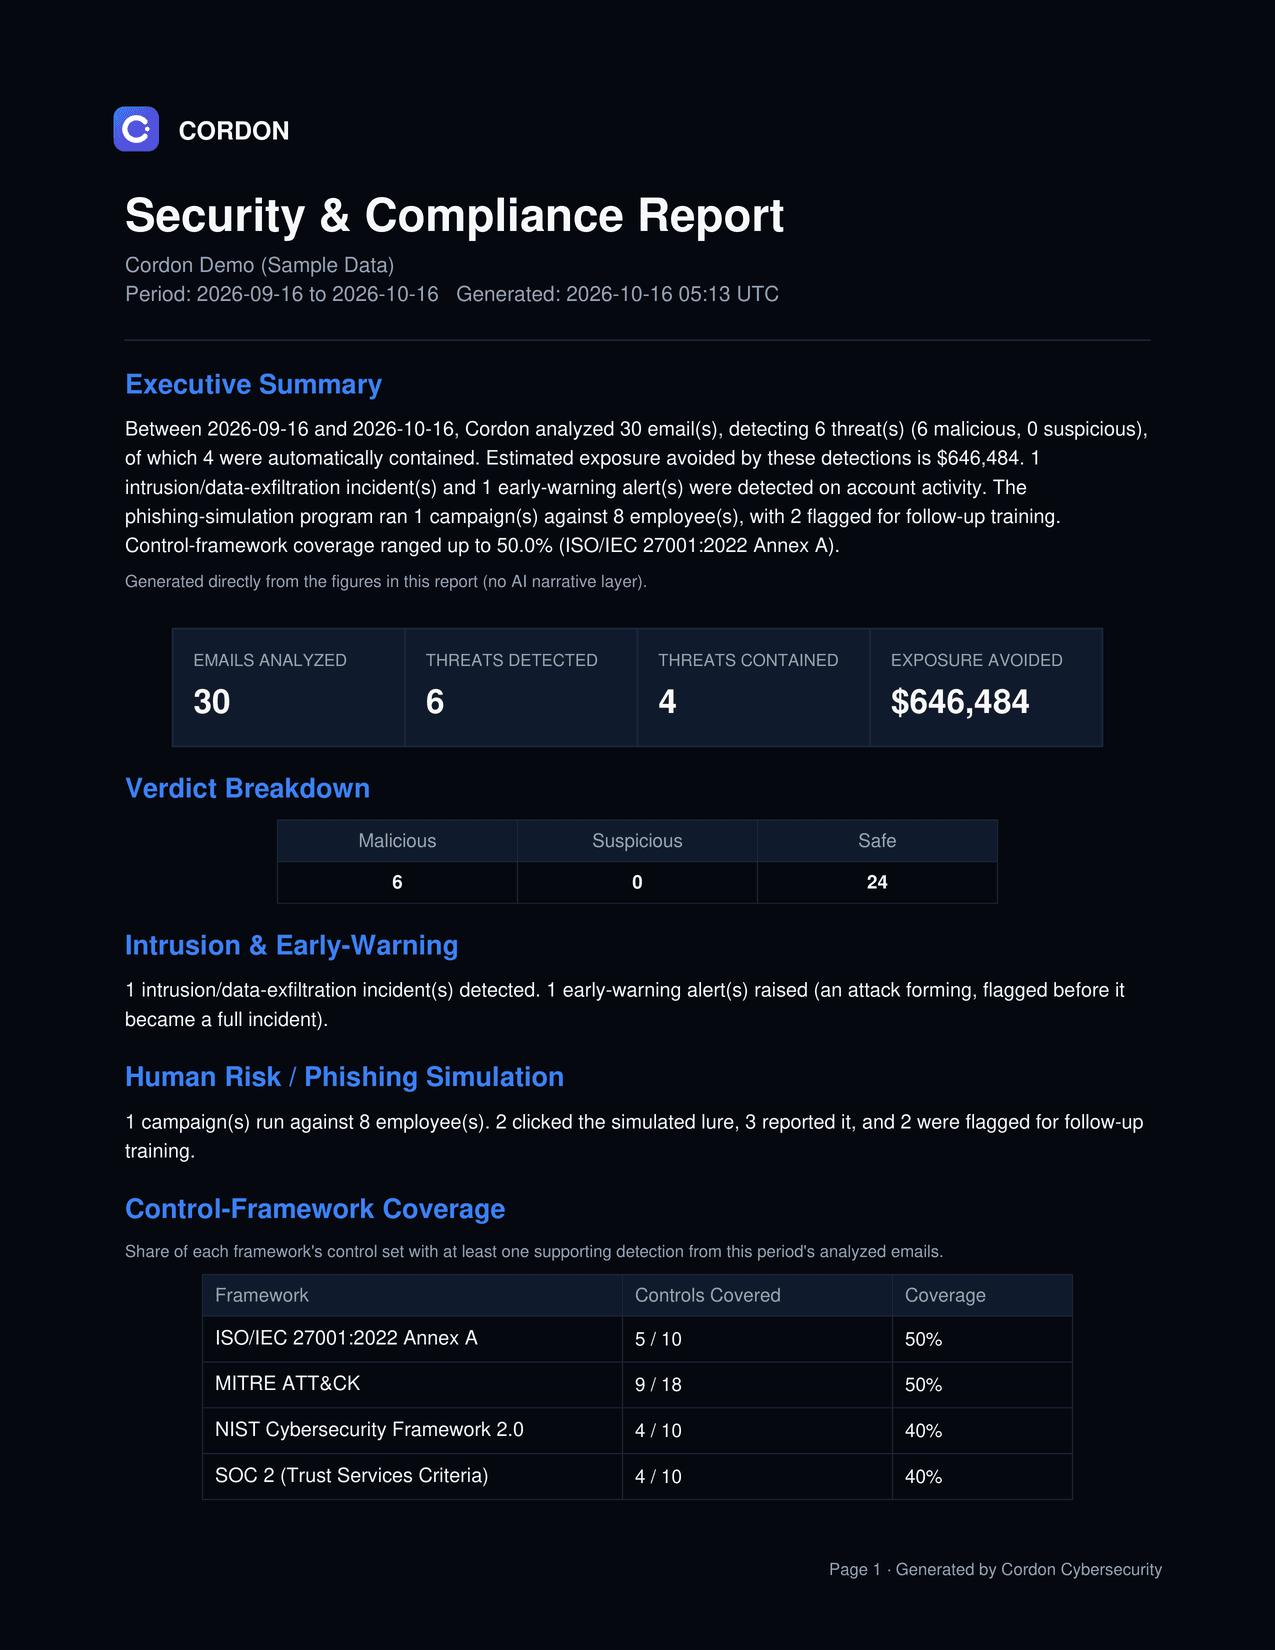
Sample report. Illustrative data.
See the attack forming, not just the aftermath.
Cordon keeps a live threat level for every account that rises as early signals accumulate: a phishing click, an unusual login, a first-time reach into sensitive files. When enough of them line up in the wrong order, it raises an “Attack Forming” alert with the full signal timeline, before it becomes a full incident. In our own testing it fired mid-chain with days of lead time before the data theft. For attacks that leave a trail in email and activity, that is the difference between responding to a breach and stopping one.
Catch the phish, and train the people it targets.
Cordon runs safe, authorized phishing simulations against your own staff, then scores each person’s human risk from how they respond. Anyone who clicks gets targeted micro-training tied to the exact lure they fell for. It is gated by design: verified domains only, admin authorization required, and no real credential is ever captured or stored. Detection protects the inbox. This makes your people harder to fool in the first place.
From flagged to fully investigated, in one step.
When Cordon flags an email threat, it does not stop at a verdict. An investigation agent automatically gathers the context: the sender’s history, related activity on the affected account, threat-intelligence matches, and the kill-chain timeline. It assembles a timeline and a scope assessment, writes a clear investigation that cites the exact evidence behind every finding, and recommends the response for you to approve. The finished investigation exports straight into your audit evidence, so the work that protects you also proves it.
See Cordon in five steps
From a landed phish to a signed audit pack: walk through the whole lifecycle.
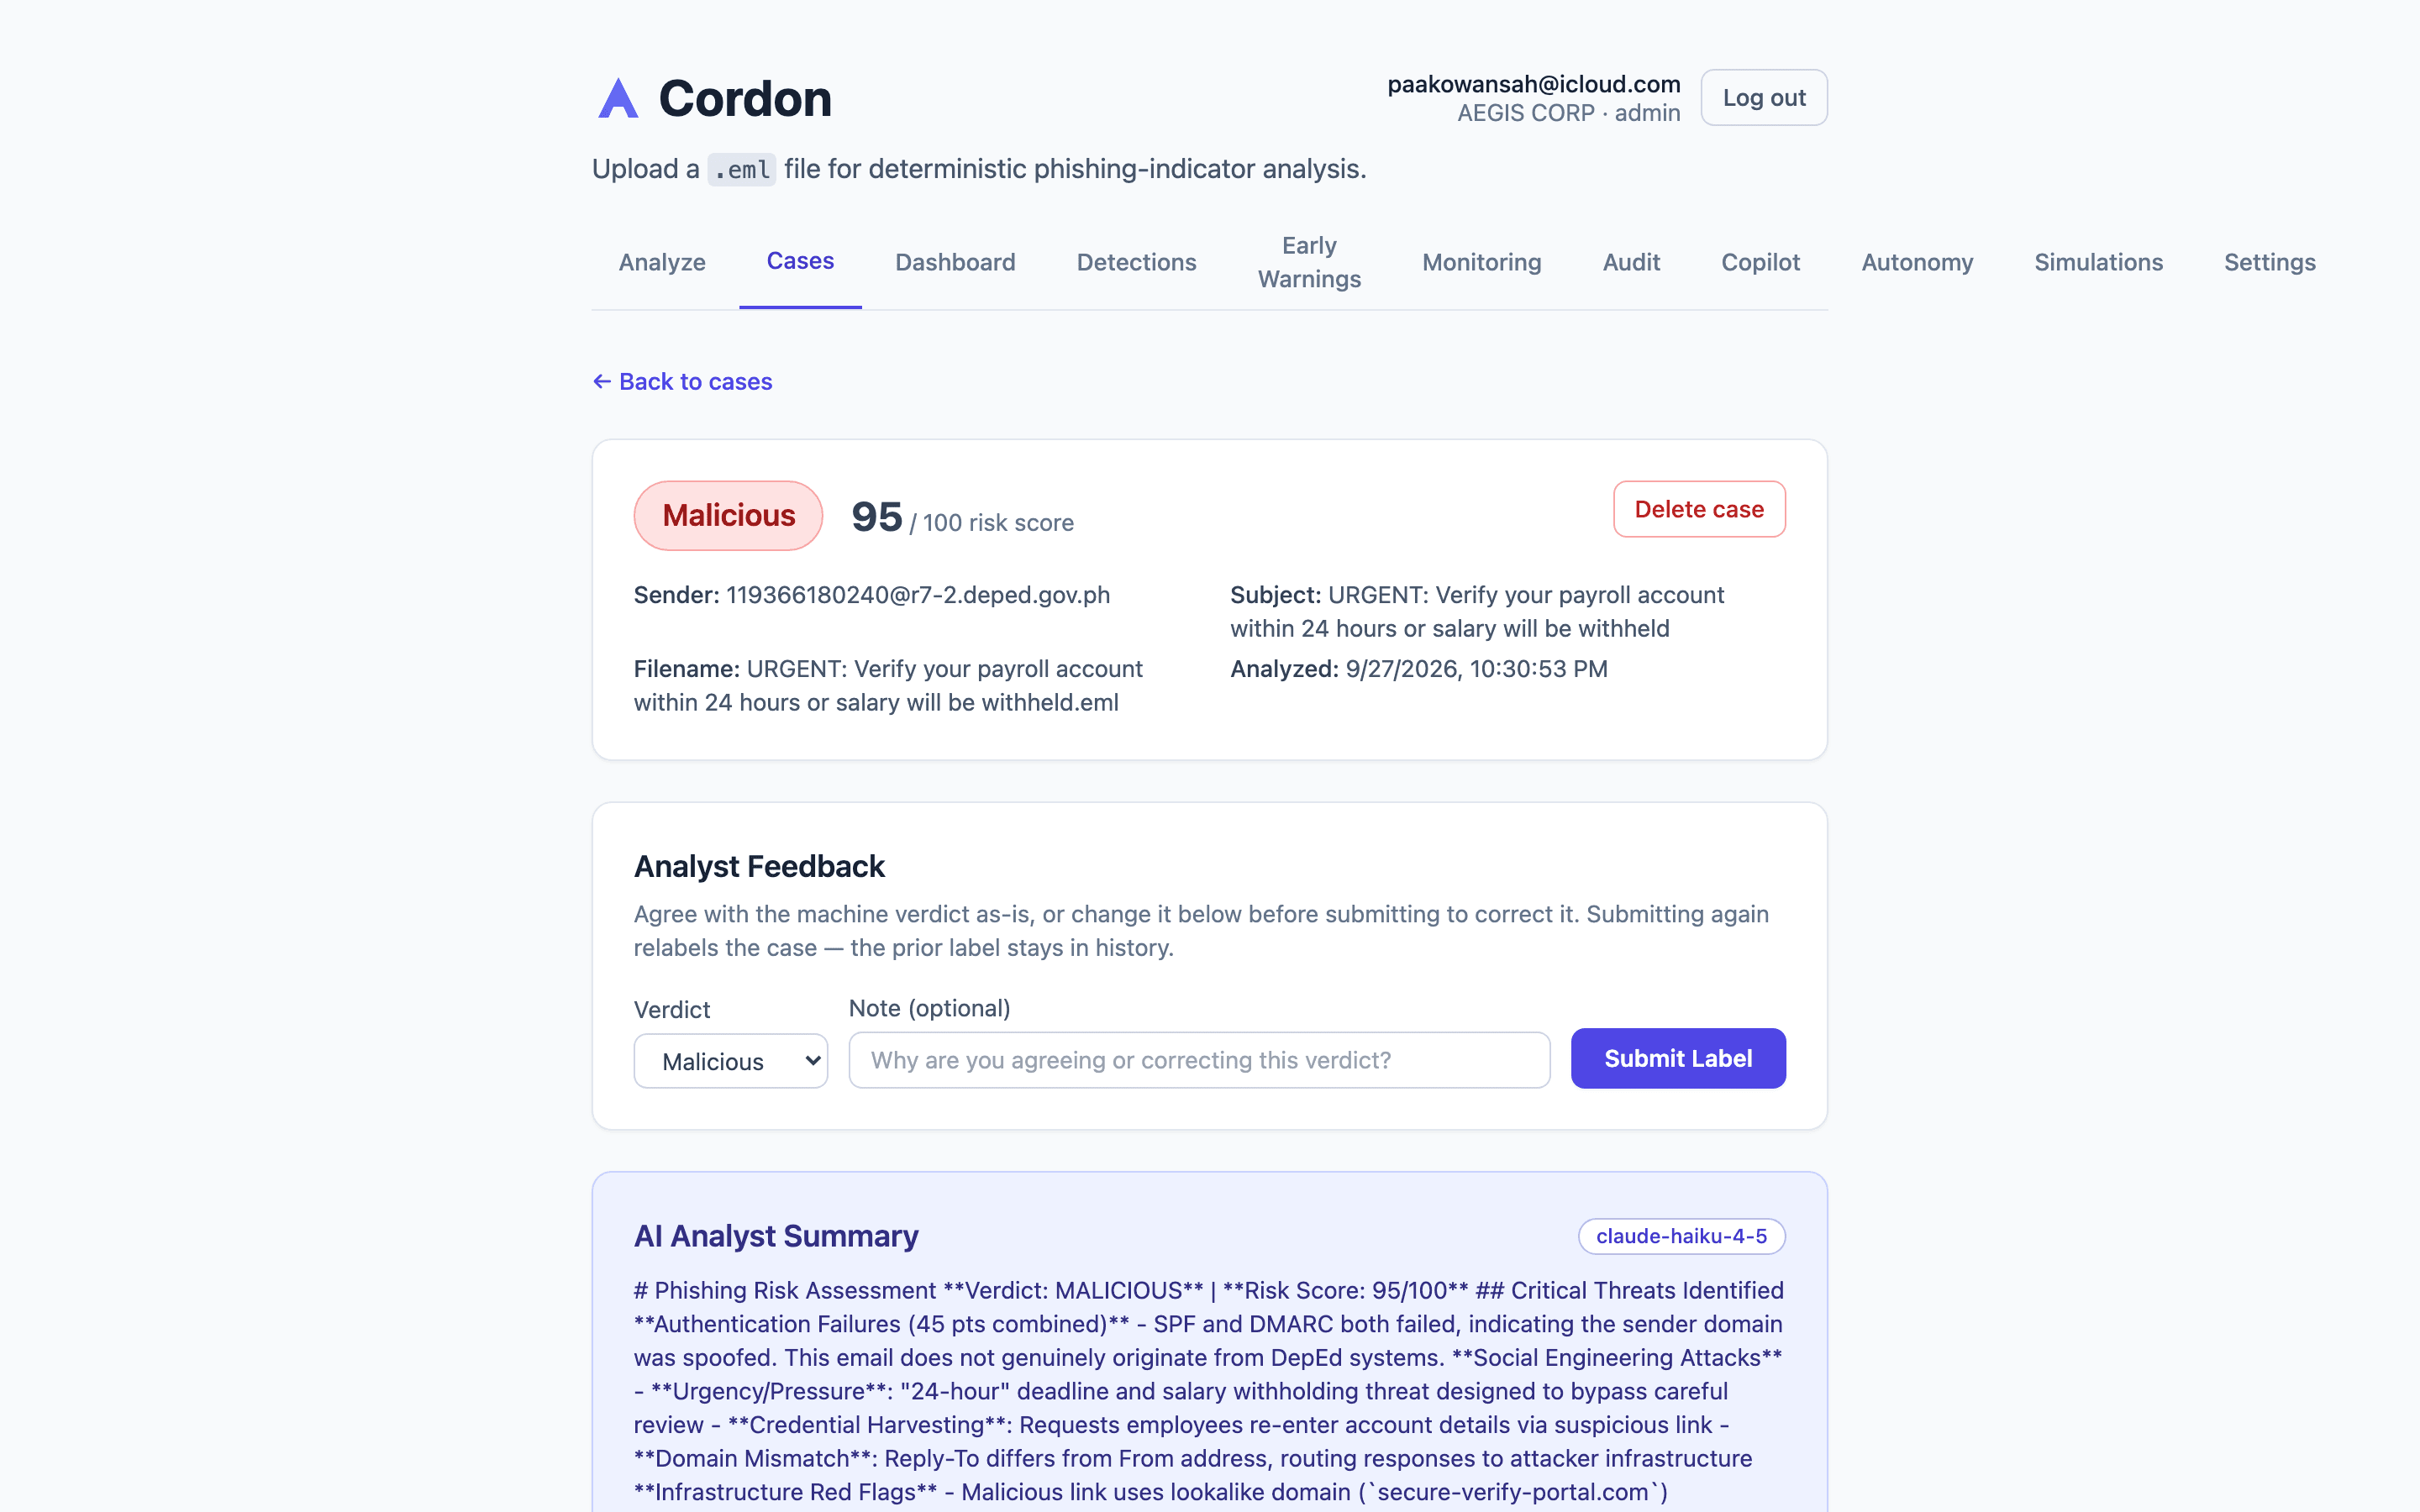
Email analysis
Every message gets a deterministic verdict plus an AI analyst narrative in under 2 seconds.
Other tools block. Cordon blocks and proves it.
- Real-time phishing verdicts, not just SPF/DKIM checks
- Behavioral baselines per user, not static thresholds
- Autonomous containment with a hard confidence floor and kill switch
- Every action auto-mapped to MITRE, NIST, ISO, and SOC 2
- One-click, board-ready and audit-ready evidence packs
Our principle
Catches phishing like a top analyst. Reports it like an auditor.
Every verdict, every containment action, and every control mapping lives in one evidence trail, from the SOC to the boardroom.
Acts on its own. Never out of your control.
Autonomy is graduated, confidence-gated, and reversible by construction, bounded at every layer, and one button away from stopping entirely.
About the Founder
Paa Ekow Ansah (Pk)
Founder, Cordon Cybersecurity AI Tool
Cordon was built by someone who came at the problem from the compliance side first.
Paa Ekow Ansah is a Governance, Risk, and Compliance (GRC) professional and certified ISO/IEC 27001 Lead Auditor. His path into cybersecurity began in cloud engineering, where he developed a real appreciation for how technical systems are built. But his strength turned out to be the discipline that sits above the technology: risk analysis, governance, and security assurance at the organizational level. That realization led him to pivot deliberately into GRC, completing an intensive GRC program with GRC Mastery and earning the ISO/IEC 27001 Lead Auditor certification.
The idea for Cordon came directly from that auditor’s lens. Trained to plan and conduct ISMS audits, assessing Annex A controls, evaluating evidence, and mapping risk treatment to real requirements, he kept hitting the same gap. Security tools are good at catching threats, but the evidence auditors actually need lives in a completely separate world. An organization could pass its audit and still be one convincing phishing email away from a breach. And when that email landed, proving what happened and which controls applied meant assembling evidence by hand.
Cordon was built to close that gap. It analyzes email the way a seasoned analyst would, then does the part most tools skip. It maps every detection to the frameworks organizations are measured against (ISO 27001, NIST CSF, SOC 2, and MITRE ATT&CK) and turns it into audit-ready evidence automatically. Detection that speaks the language of compliance. Put simply: it catches phishing like a top analyst, and reports it like an auditor.
Expertise
Auditing & Assurance
ISMS & Governance
Risk Management
Compliance & Standards
Help shape Cordon: get early access
We’re working closely with a small group of security teams to refine detection, autonomy, and audit workflows. Join as a design partner and shape what ships next.
Book a 20-minute demo